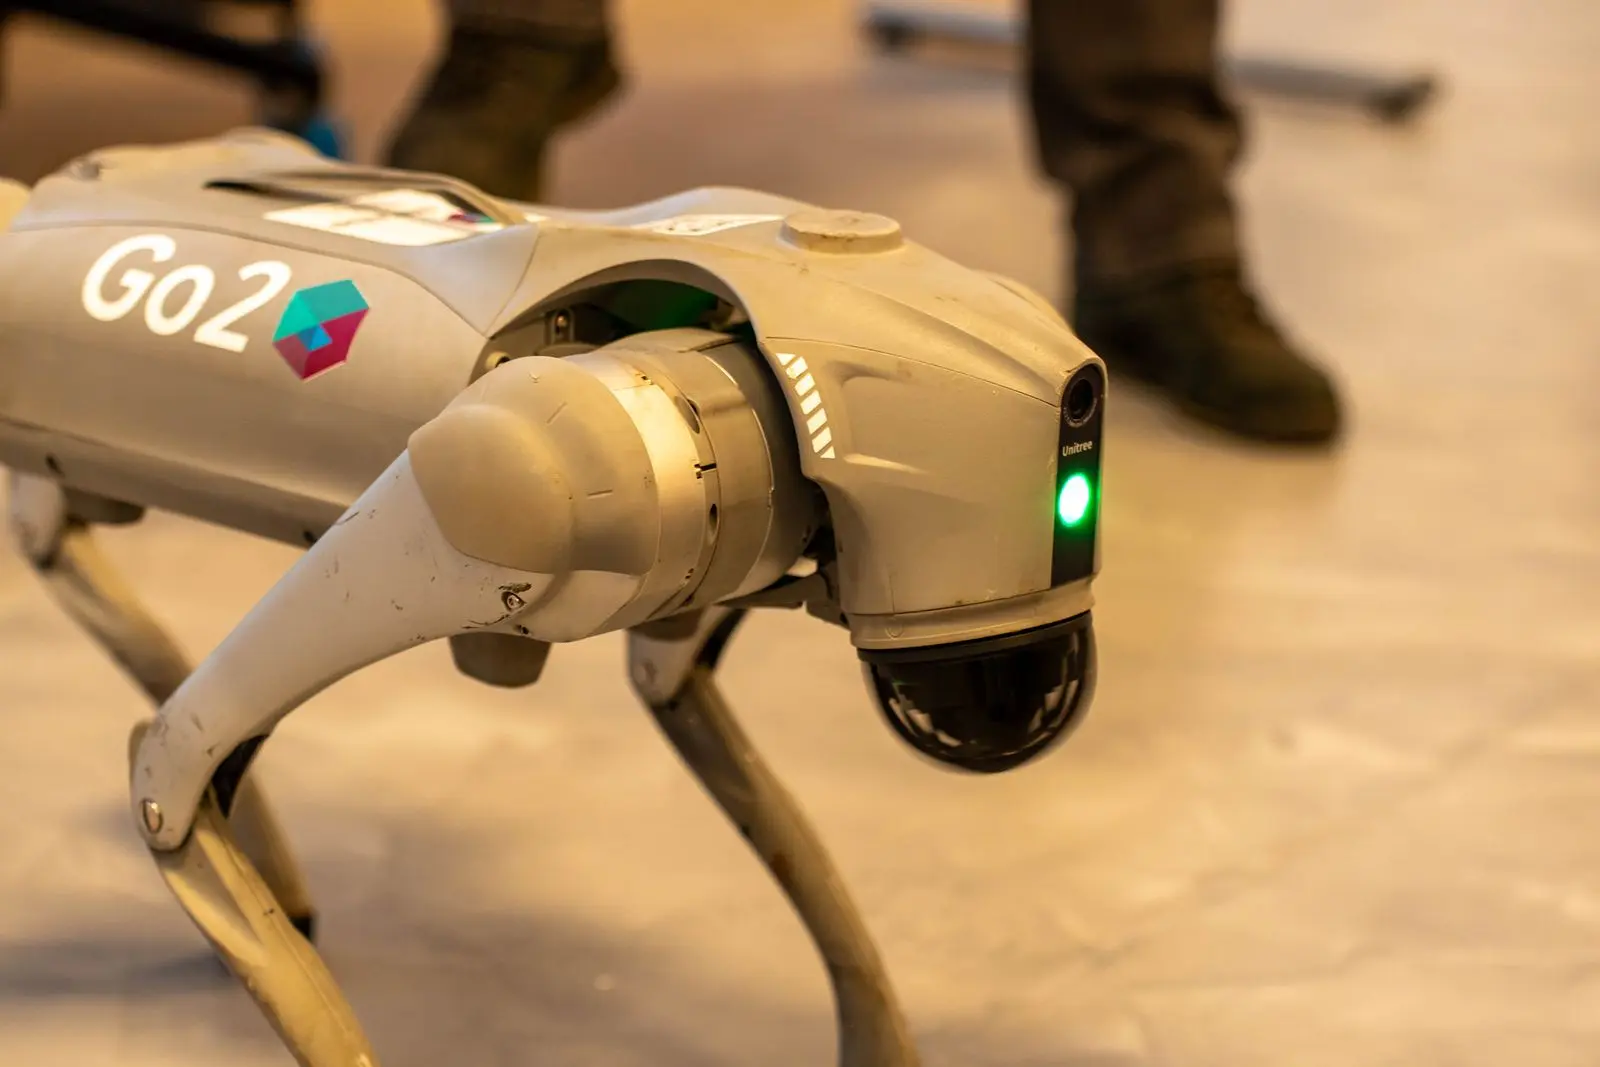
A critical Unitree Go2 vulnerability was published on October 24 with a severity score of 9.6 out of 10. The flaw is tracked as CVE-2026-115995, according to TheHackerWire’s advisory write-up. It affects Go2 robots running firmware up to version 1.1.11.4. Version 1.1.11.5 or later is listed as the fix.
The Go2 is a four-legged robot dog sold by Unitree Robotics, a Chinese robot maker. Owners who have not updated their firmware should check which version their robot runs.
Key facts about the Unitree Go2 vulnerability
| Item | Detail |
|---|---|
| Identifier | CVE-2026-115995 |
| Severity | 9.6 (Critical) |
| Flaw type | OS command injection (CWE-78) |
| Component | chat_go, in gpt_thread.py |
| Affected firmware | Up to 1.1.11.4 |
| Fixed firmware | 1.1.11.5 or later |
| Published | October 24, 2026 |
What command injection means
Command injection is a class of bug where a program passes outside input to the operating system without checking it. The system then reads that input as a command. The scoring scale for these bugs runs from 0 to 10, and scores from 9.0 to 10 count as critical. A 9.6 sits near the top of that band.
What the flaw does
The bug sits in a part of the Go2 firmware called chat_go. Inside it, the set_volume function does not check its Value input properly. An attacker can place system commands in that input. The commands then run with the same privileges as the chat_go process.
In this Unitree Go2 vulnerability, the weak point is a volume setting. That is an ordinary feature, which shows how a small input field can become an entry point. The write-up says successful exploitation could lead to full control of the robot or serious data compromise. It describes the attack as remote, over the robot’s network interface. It does not publish a scoring vector, so details such as attack complexity are not confirmed.
Is it being exploited?
The advisory reports no evidence of attacks in the wild. It says no public proof-of-concept code was indexed at the time of writing. It also says the flaw is not on the list of known exploited vulnerabilities kept by the U.S. cyber agency CISA, and that exploit scoring was still pending.
Those points describe the situation on October 24. They can change. Owners should treat the lack of public exploits as a snapshot, not a guarantee.
What Go2 owners can do
The listed fix is a firmware update to version 1.1.11.5 or later. Until the robot is updated, keeping it off shared or public networks lowers the chance that someone can reach its interface.
Network separation is a common step for connected devices. A robot on a guest network cannot reach, or be reached by, laptops and phones on the main network. That limits the damage if a device is compromised.
A single-source report
Everything about the Unitree Go2 vulnerability rests on one source. TheHackerWire’s page is the only reference it cites. It links no vendor advisory, no CVE database record and no patch notes. The Jolt Journal has not confirmed the details with Unitree. The firmware numbers and the 9.6 score should be checked against Unitree’s own notices and the official CVE record when those appear.
For other recent examples of critical flaws and the patches that followed, see the Jolt Journal’s reports on the GitLab vulnerability that scored a perfect 10 and the Ivanti Connect Secure zero-days.
What to watch
Three things would settle open questions about the Unitree Go2 vulnerability. The first is a vendor notice from Unitree that confirms the affected and fixed versions. The second is an official record in the National Vulnerability Database. The third is any sign that attackers are using the flaw. Until then, the safest step for owners is to update and to keep the robot on a separate network.