We may earn a commission when you buy through links on this page. It doesn't change what we recommend.
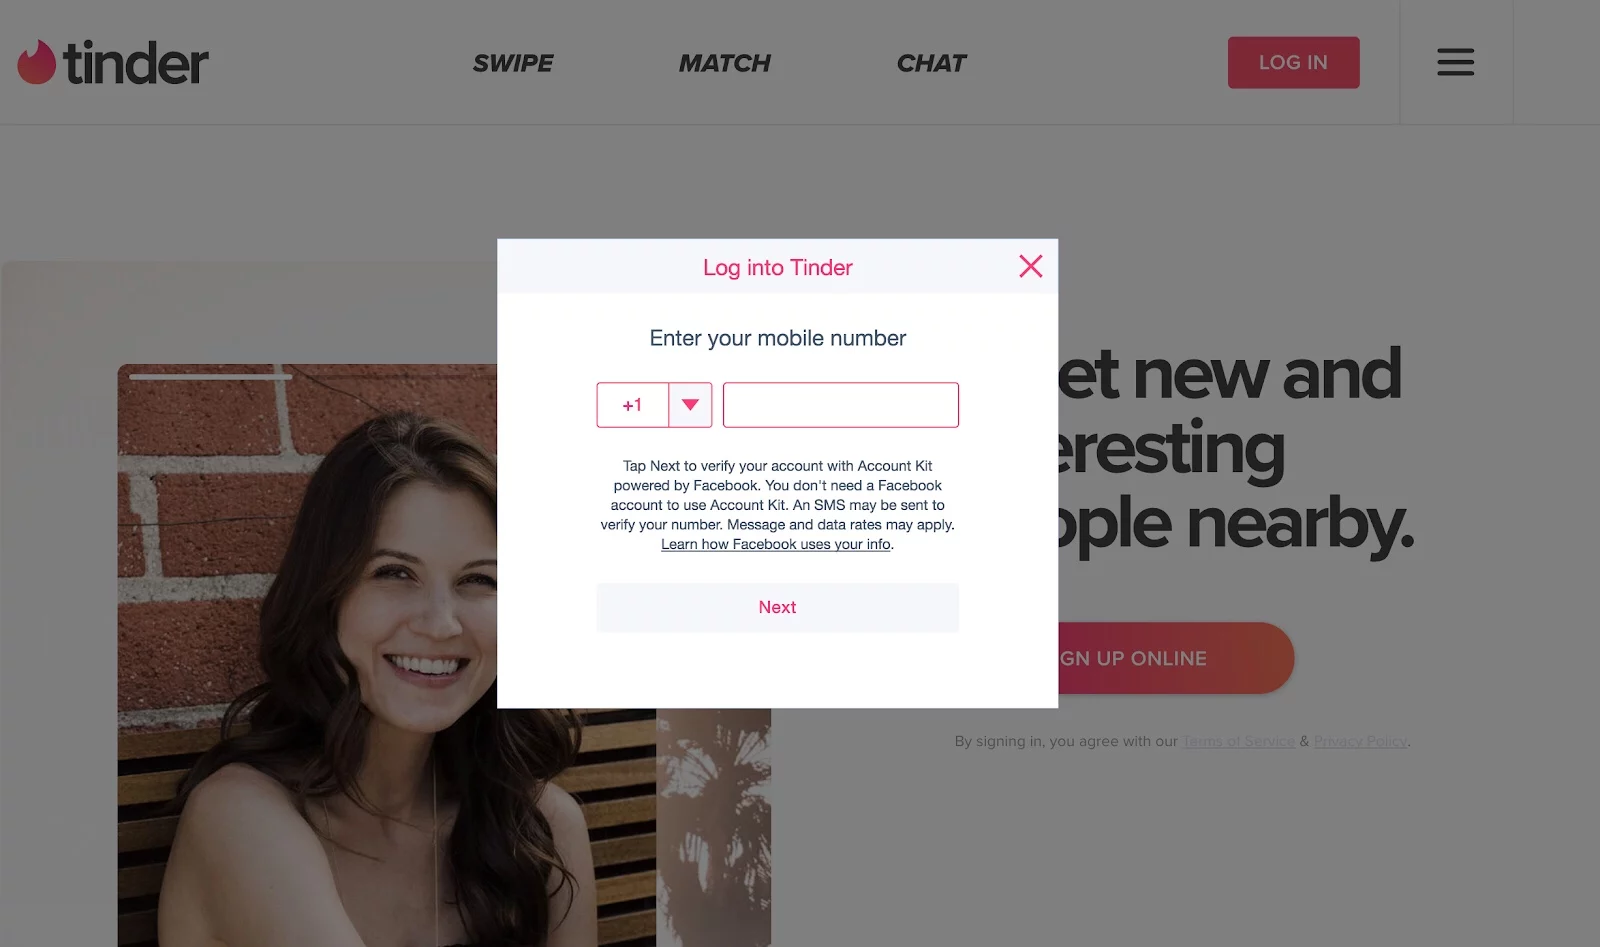
Tinder was previously hit with a big security flaw that allowed access to accounts with just a phone number. Security researchers at Appsecure discovered a way to access anyone’s Tinder account just by their phone number. The exploit in question took advantage of a software flaw in both Tinder’s app login process as well as Facebook API that it was based on.
The issue has since been fixed, but knowing that this exploit existed is a big security lapse. “Both the vulnerabilities were fixed by Tinder and Facebook quickly,” write Appsecure’s Anand Prakash on Medium. To reward for Appsecure’s efforts, both companies gave $5000 and $1250, respectively, for its findings and report.
Mind you, this isn’t the first time a report came out stating a Tinder security flaw. Back in 2014, the company failed to encrypt user photos and exposed users’ exact locations for months, which again is a huge oversight that should have been checked and covered.
https://youtube.com/watch?v=tIAxmZt1joY